Where provider keys go to get lost
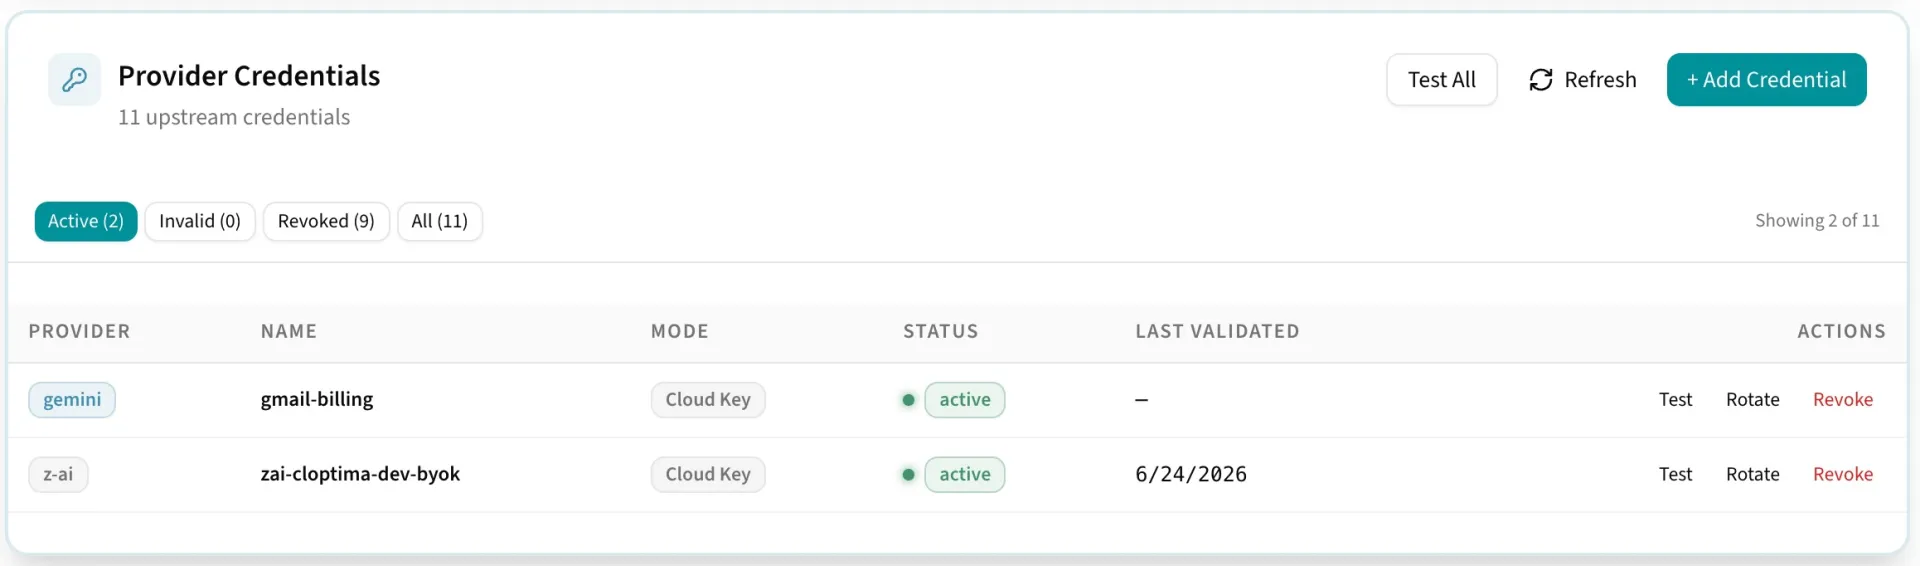
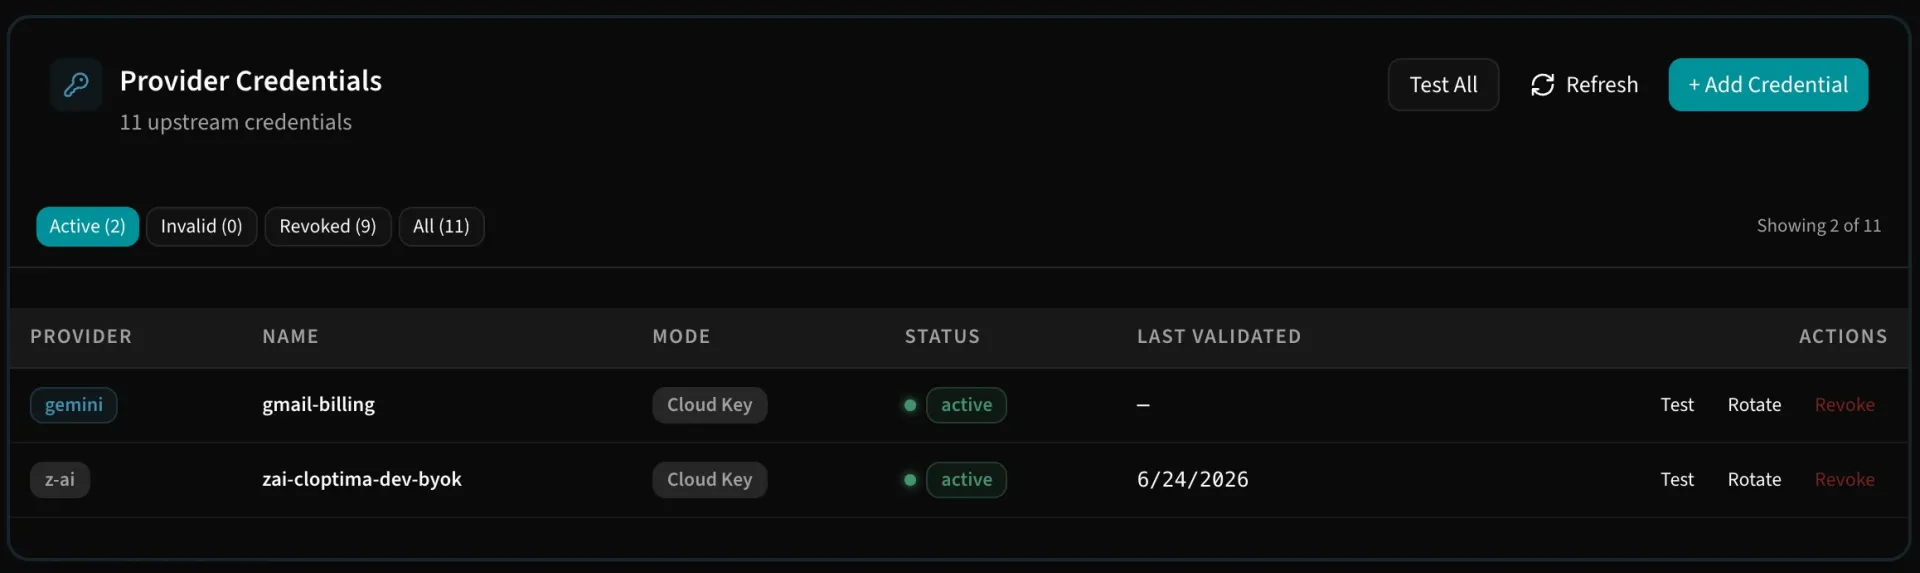
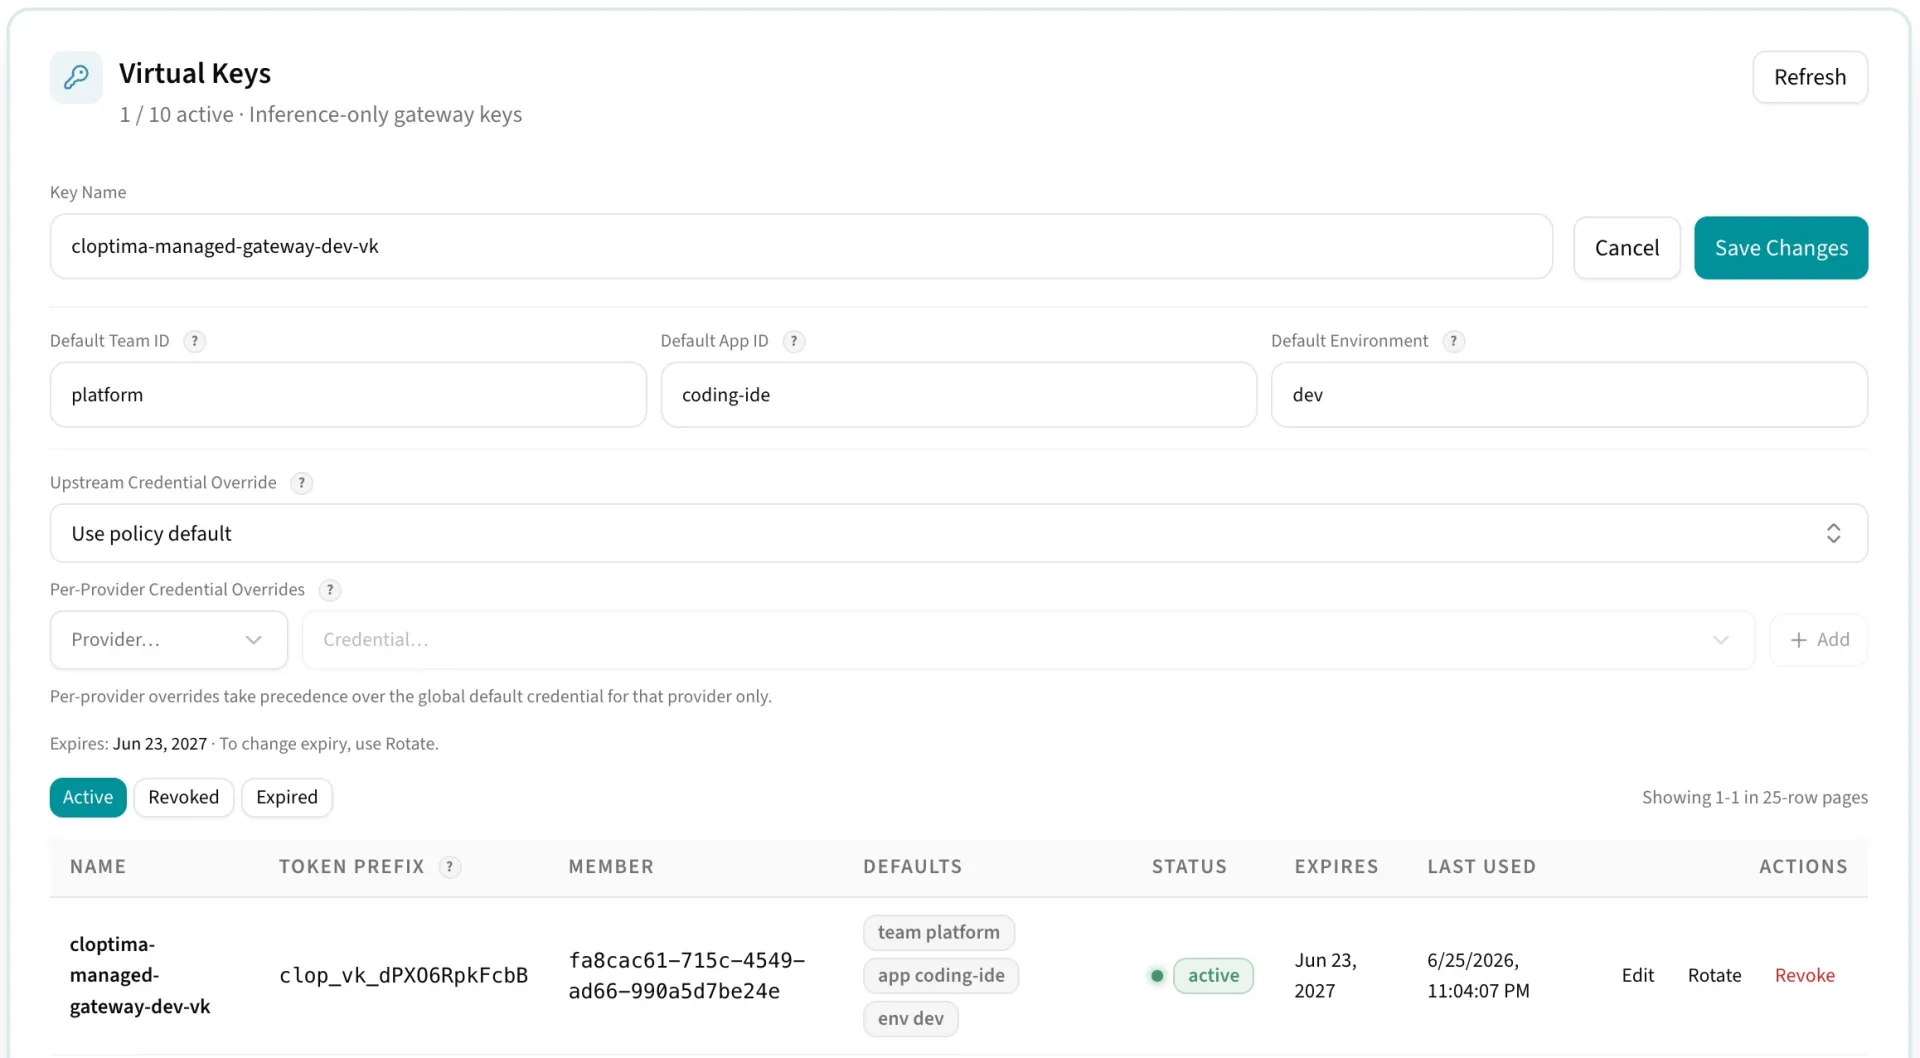
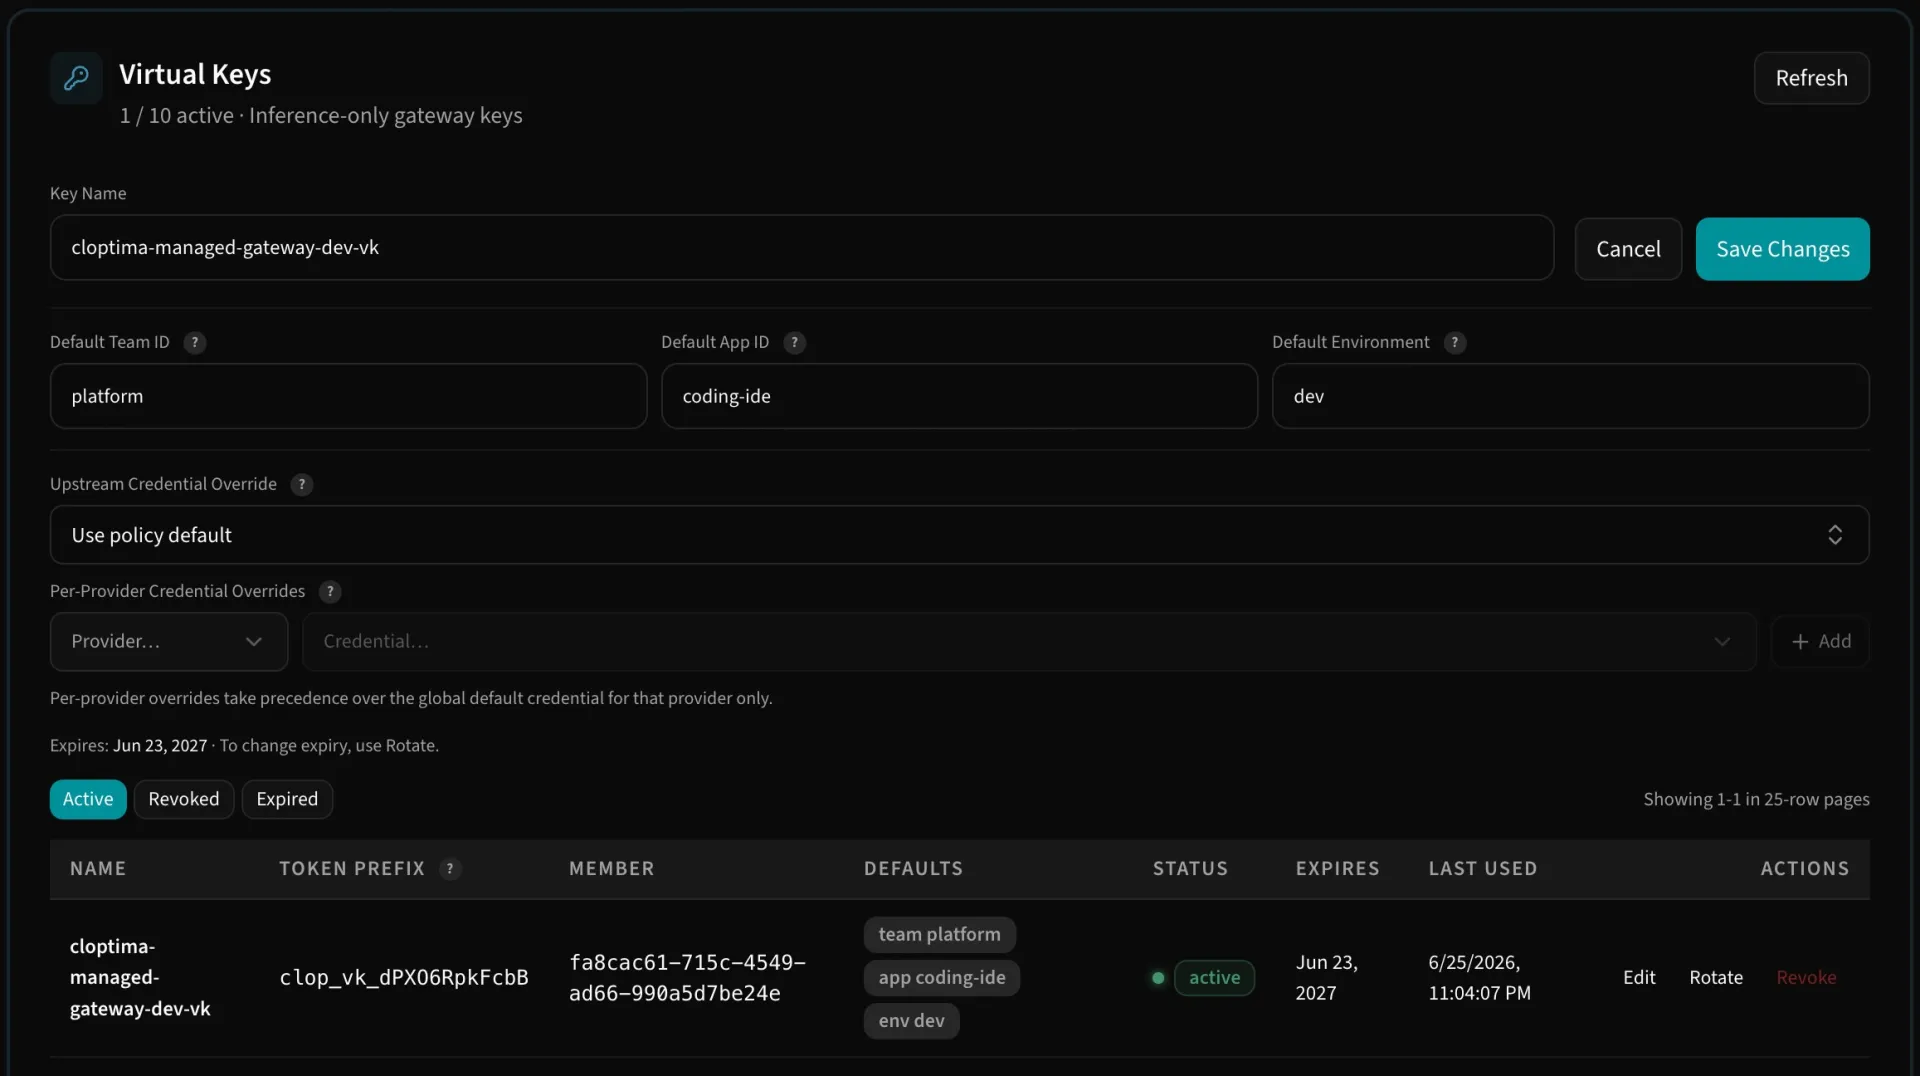
Provider keys often live in app repos, CI variables, local machines, and team-specific vaults. That makes rotation, access review, and model policy enforcement harder than it should be.
- Credential sprawl across teams
- No clean view of which app uses which provider key
- Hard-to-audit access to premium models
- Manual rotation and weak ownership